

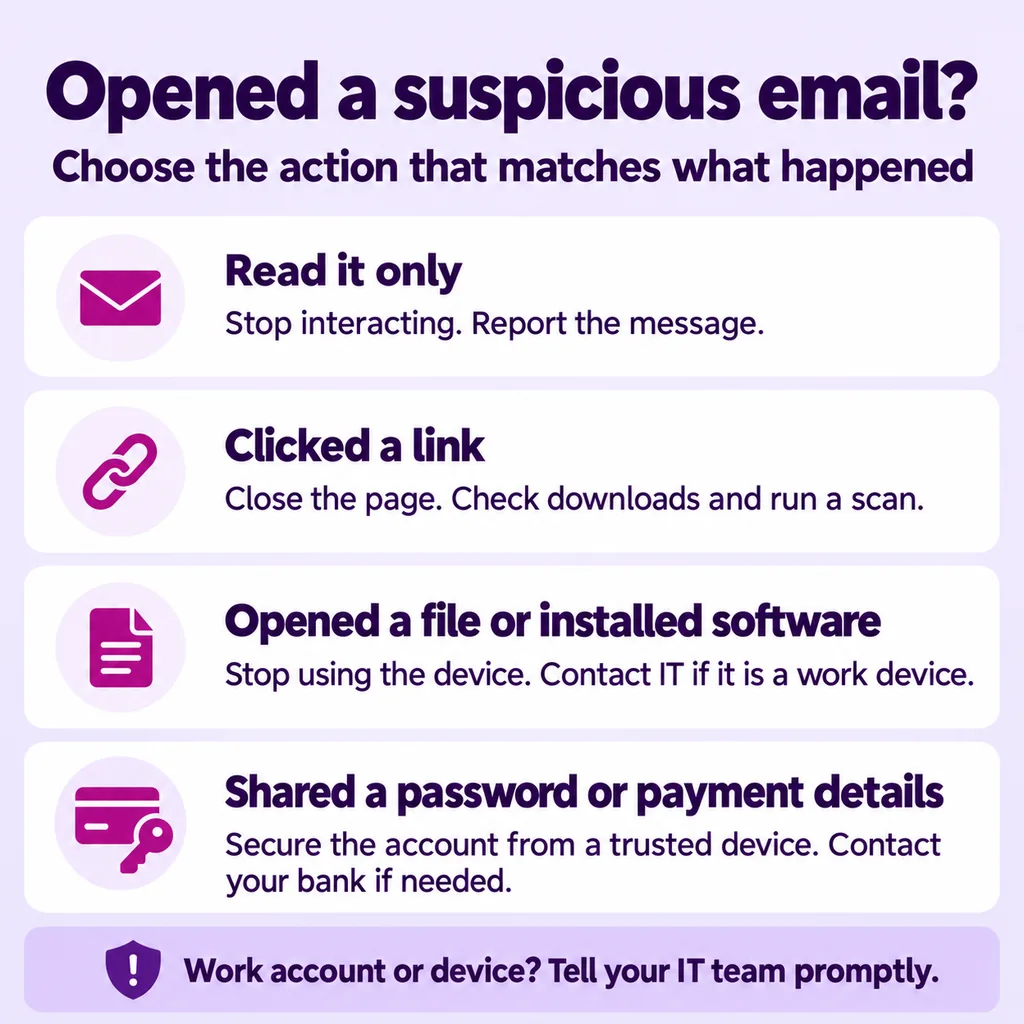
If you only opened a spam email, your device is usually at low risk when your email app and operating system are up to date. Reading a message is different from clicking a link, opening an attachment or giving someone your password. Stop interacting with the message and use the checklist below. If you shared bank details or approved a payment, contact your bank immediately using its official app or a number you already trust.
Do not assume that every unexpected email is harmless, or that one accidental click means you have been hacked. The useful question is: what did you actually do after opening it? If this involves a work account or device, tell your IT team promptly.
Security guidance checked: 8 October 2026. These steps follow current public guidance; they are not a diagnosis of your device.
Opened a spam email? Start here
| What happened? | What to do now |
|---|---|
| You read or previewed the message only | Stop interacting. Report it as spam or phishing, then delete it after any reporting or evidence instructions. |
| You clicked a link or scanned its QR code | Close the page. Check whether anything downloaded. Run a full antivirus scan and follow the relevant rows below. |
| A file downloaded, but you did not open it | Do not open or preview it to investigate. Ask IT on a work device; otherwise scan and quarantine or remove the suspicious file. |
| You opened a file, enabled macros or installed software | Stop using the device for sensitive tasks. Contact IT if it is a work device. If malware is suspected, disconnect its network connection and get help. |
| You entered a password, shared a code or approved an unexpected sign-in | Use a trusted device to secure the account, end other sessions and review its security settings. |
| You shared card details or sent money | Contact your bank immediately through a known channel. Report fraud using the routes below. |
The NCSC response guidance recommends different responses for exposed passwords, suspicious links or software, and money or banking details. Follow more than one route if several things happened.
- Opened a spam email? Start here
- What happens if you open a spam email?
- What to do if you accidentally open a spam email
- What to do if you clicked a suspicious link
- What to do if you opened a phishing email without clicking anything
- What to do if you shared a password or approved access
- How to report a spam or phishing email in the UK
- How to prevent this from happening again
- Common questions about opening spam emails
- Final thoughts
What happens if you open a spam email?
Spam is unwanted email. Phishing is an attempt to make you reveal information or take an action that benefits an attacker. A message can be both. Our phishing guide explains common examples.
Simply reading a message does not normally run an attached program or hand over your password. However, no email app is completely immune to security flaws. Keep the app, browser and operating system updated, and take provider warnings seriously.
Remote images can act as tracking signals. That is a privacy issue, not proof that malware has installed. It also depends on the email service: Google explains that Gmail protects against some image-based information collection, while senders may still sometimes know that you opened a message. An open does not prove your address has been sold or guarantee that more spam will follow.
What to do if you accidentally open a spam email
- Stop interacting: do not reply, click links, scan QR codes or open attachments.
- Use your provider’s report spam or report phishing option. Reporting helps its filtering; it does not guarantee that all future messages will be blocked.
- If it involves work, follow your organisation’s reporting process. Tell IT what happened before deleting evidence.
- Check that your email app, browser and operating system receive updates. If you only read the email and nothing else happened, a password reset or factory reset is not normally the first response.
Do not use an unfamiliar message’s unsubscribe link to test whether it is genuine. For a newsletter you recognise and deliberately subscribed to, use the provider’s unsubscribe controls or visit the organisation’s website independently.
What to do if you clicked a suspicious link
Close the page without entering anything else. Check your browser’s downloads list without opening suspicious files. A click alone is not evidence that malware installed, but a page may try to download a file or persuade you to install software, sign in or grant permissions.
Run a full scan with your security software, as recommended in the NCSC guidance linked above. On a Windows device using Microsoft Defender, open Windows Security → Virus & threat protection → Scan options → Full scan → Scan now. Microsoft documents these scan options. If another antivirus provider manages protection, use its scan controls instead. Our Windows 11 antivirus guide explains the protection options.
Think beyond passwords: did you allow browser notifications, approve an app’s access to your account or accept a sign-in request on your phone? Remove unfamiliar permissions through the real account or browser settings. Do not revisit the suspicious page to undo them.
What to do if you opened a spam email attachment
Downloaded but not opened? Do not open it to see what it is. On a personal device, scan it and follow your security software’s quarantine or removal advice. On a work device, report it and let IT decide what evidence to retain. A downloaded file is not automatically a program that has executed.
Opened, ran or installed it? Treat the device as potentially compromised, especially if you enabled macros, accepted an installer or gave remote access. Files can exploit vulnerable software, so the file extension or familiar icon is not a safety test.
- Stop using that device for banking, email and password changes. Use a separate trusted device for account recovery.
- If malware is suspected, disconnect Wi-Fi or the network cable to limit further communication. For managed equipment, contact IT using another device and follow its incident instructions.
- Update and scan with trusted security software where appropriate. Follow its remediation instructions; persistent alerts or unusual behaviour need specialist help.
- Do not wipe a work device, uninstall evidence or restore backups before IT advises you. Record the time, message subject and what you opened or installed.
Disconnecting a device does not undo information already stolen, and a clean scan does not establish that an online account is safe. Our guide to Trojan malware explains why a file can look legitimate while carrying an unwanted function.
What to do if you opened a phishing email without clicking anything
If you read it but did not follow links, open files, reply with information or approve a request, use the read-only steps above. You do not need to investigate the sender by clicking its links. To check an account warning or invoice, open the organisation’s official app or type its known address yourself.
You can limit remote-image loading where your mail app supports it. Gmail offers an “Ask before displaying external images” setting on the web; classic Outlook has separate automatic picture-download controls. Settings differ between clients, and blocking images does not make links or attachments safe.
What to do if you shared a password or approved access
Act even if the page showed an error afterwards. It may already have received what you typed. Use a trusted device and reach the provider through its official app or website, not a link in the message.
- Change the exposed password and any other account that reused it. If you cannot sign in, use the provider’s official account-recovery process.
- Review recent security events and signed-in devices. End unfamiliar sessions and use the provider’s sign-out-everywhere option where available.
- Check recovery email addresses, phone numbers and authentication methods. Remove changes you did not make, then enable two-step verification.
- Review third-party apps and account permissions. If you granted access to a malicious app, revoke that access; changing a password alone is not a substitute.
- Check mailbox forwarding, filters or inbox rules, and Sent and Deleted folders. Unexpected rules can hide security warnings or copy messages elsewhere.
These checks are covered in Google’s compromised-account guidance. For a work Microsoft 365 account, ask IT to investigate sessions, authentication methods, app consent and mailbox rules using Microsoft’s incident-response guidance. Some checks require administrator access.
Do not assume sign-out is instant: Microsoft says its personal-account sign-out-everywhere process can take up to 24 hours. If your account sent scam messages, warn affected contacts through a separate trusted channel. The NCSC account-recovery guide also covers checking forwarding and alerting contacts.
How to report a spam or phishing email in the UK
- Suspicious email: forward it to [email protected], the Suspicious Email Reporting Service. GOV.UK explains the reporting route. You do not need to click a link or download an attachment to report it.
- Your email provider: use its report spam or phishing controls as well. Menu names vary between apps; reporting and blocking a sender serve different purposes.
- Work email: use the approved reporting button or contact IT. Do not forward confidential company material to a personal mailbox to investigate it.
- Financial details or money: contact your bank immediately through its official app or a known number. Preserve the message and transaction information.
- Fraud: current NCSC guidance directs people in England, Wales and Northern Ireland to Report Fraud; in Scotland, contact Police Scotland on 101. Follow the bank’s instructions too.
When asking for help, give a short factual account: when it happened, the account and device involved, whether you clicked or opened anything, and what information or permissions you supplied. Do not send anyone your password, recovery codes or full card details as evidence.
How to prevent this from happening again
- Keep operating systems, browsers and email apps updated. Use supported software and current security protection.
- Use unique passwords and enable two-step verification. Never approve an unexpected sign-in prompt or share a one-time code in response to an email.
- Verify urgent payment, password-reset and account-warning requests through a separate known channel. A familiar display name, polished wording or padlock icon is not proof of a trustworthy request.
- Pause before installing software, enabling macros or authorising an app. Check what the requested permission actually allows.
- Make reporting easy for colleagues and family. Someone who reports an accidental click promptly gives responders a clearer chance to contain it.
For a broader routine, see our practical cybersecurity tips. The aim is to reduce exposure and respond sensibly, rather than promise that any single setting prevents every scam.
Common questions about opening spam emails
Can opening a spam email give you a virus?
Usually, simply reading a message in an updated app is lower risk than opening a file or running software. Security flaws can still exist, so keep software patched. If an attachment opened automatically or your security software warned you, follow the attachment-response steps.
Should I change my password if I only read the email?
Reading alone does not normally expose a password. Change it if you entered it on a suspicious page, disclosed it, see unauthorised activity or your provider or IT team advises you. Secure reused passwords too.
Does deleting the email fix the problem?
Deleting removes the message from your inbox. It does not remove installed malware, reverse a payment or end an attacker’s account access. Report first and follow the response that matches what happened.
What if I replied with personal information?
Stop the conversation. Record what you shared and tell the relevant organisation through a known channel. Banking details require prompt bank contact; passwords or codes require account recovery. Be alert for convincing follow-up messages that use the information you disclosed.
Final thoughts
Match the response to the action. Reading an unwanted email usually calls for reporting and caution. Clicking, opening a file, sharing credentials and sending money each need different checks. If several happened, follow each relevant route and tell your IT team when work systems are involved.
Lets Talk!
If you have additional comments or questions about this article, you can share them in this section.